
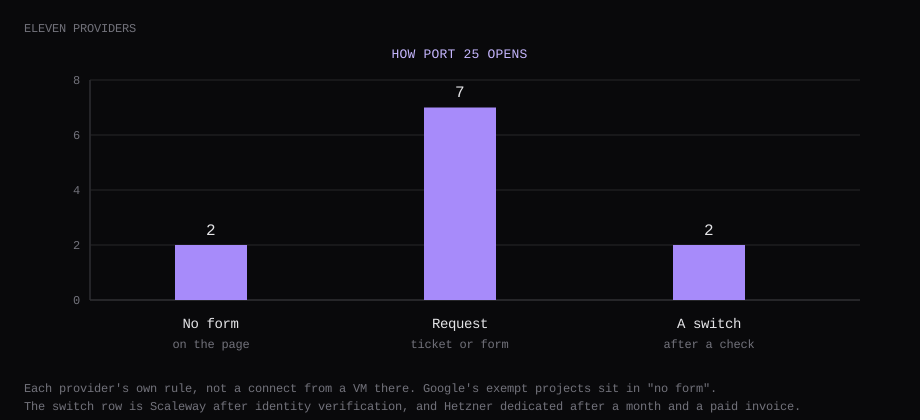
Outbound port 25 starts closed at all eleven of these providers. Seven open it only after you ask: Oracle Cloud for tenancies created after 23 June 2021, Hetzner Cloud, Vultr, Linode on some accounts created after 5 November 2019, Amazon Lightsail, EC2, and OVHcloud VPS. Two let you throw the switch yourself after a condition: Scaleway, once identity verification is done, and a Hetzner dedicated server, once the account is a month old and the first invoice is paid. DigitalOcean blocks 25, 465 and 587 on every Droplet, including traffic through a Reserved IP, and will not open them. Google Compute Engine blocks port 25 when the destination is outside the VPC. Some projects are already exempt, and there is no form to ask.
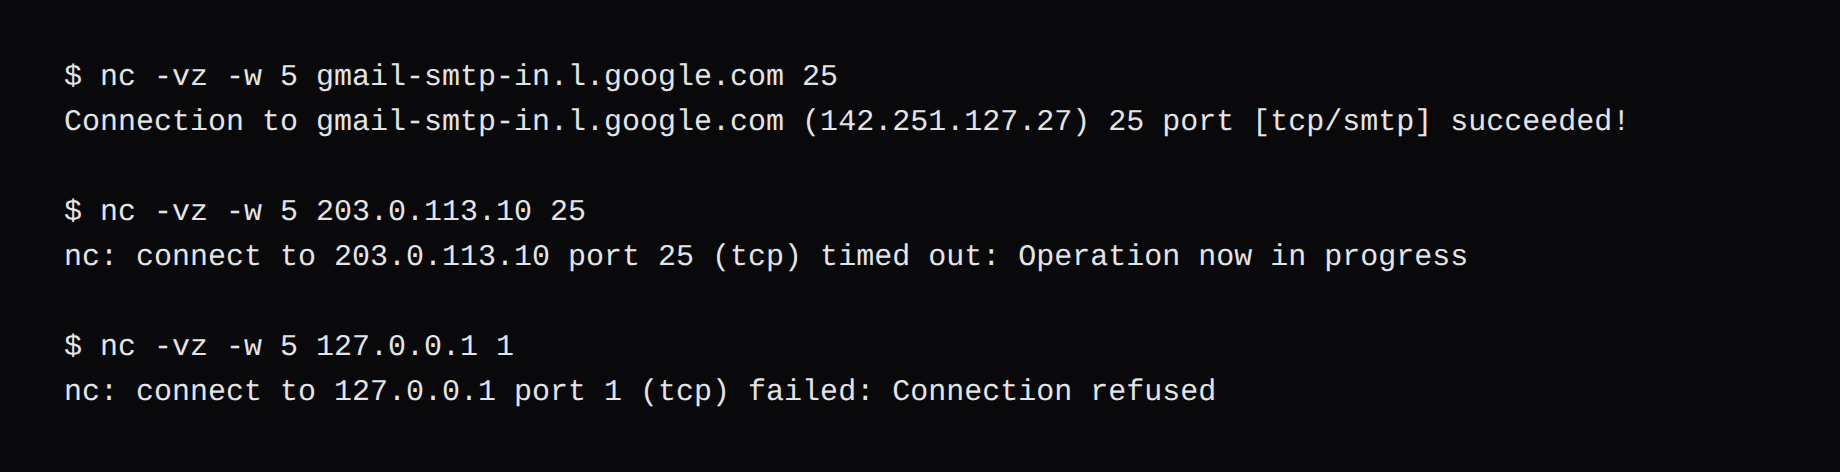
A connect from this guest reached Gmail, Outlook and Yahoo on port 25. That is this network, not a machine at those providers.
Is port 25 blocked on my VPS
The check is one connect, with a five-second wait.
nc -vz -w 5 gmail-smtp-in.l.google.com 25A timeout means the packets were dropped, or nothing answered. A connection refused means some machine sent a reset. A provider SMTP block is the first of those. A port with nothing listening, on a path that is open, is the second.
203.0.113.10 is a documentation address from RFC 5737. Nothing answers there, so a connect with -w 5 is the shape of a drop. 127.0.0.1 port 1 is a closed port on this machine, and it answers with a reset. Gmail's MX answered.
The same guest also reached outlook-com.olc.protection.outlook.com, Yahoo's MX mta7.am0.yahoodns.net, and smtp.gmail.com on 587. Port 587 is submission. You authenticate to a relay, and the relay speaks port 25 to the rest of the internet. Several of these providers leave 587 open while they block 25. DigitalOcean, a restricted Linode account, and Scaleway before the checkbox block 587 as well. A timeout on 25 and a success on 587 is Hetzner's published split. A timeout on both is DigitalOcean's.
Which providers block port 25
| Product | Blocked by default | How it opens | Source |
|---|---|---|---|
| DigitalOcean Droplets | 25, 465 and 587, including Reserved IPs | No way to open it | Why SMTP is blocked |
| Google Compute Engine | 25 to destinations outside the VPC. 587 and 465 are unrestricted | Some projects are already exempt. No request form | Sending mail |
| Oracle Cloud | 25, for tenancies created after 23 June 2021 | A service limits request | Release note |
| Hetzner Cloud | 25 and 465. 587 stays open | A limit request, after one month and a paid invoice, decided per account | Cloud FAQ |
| Hetzner dedicated | 25 and 465. 587 stays open | You unblock it in Robot after one month and a paid invoice. Sooner than that, a contact form, weekdays 08:00 to 18:00 | Robot FAQ |
| Vultr | 25 on new instances | A support ticket, decided per case. They point 465 and 587 at an external relay | Why SMTP is blocked |
| Linode, on Akamai | 25, 465 and 587, on some accounts created after 5 November 2019 | A support ticket: your name, the use, the domains, and a public link | Send email on Akamai Cloud |
| Scaleway Instances | 25, 465 and 587 | Identity verification, then Enable SMTP on the security group | Send emails from an Instance |
| Amazon Lightsail | 25 | The email-limitation form, signed in as the account root, one request per region | AWS re:Post says up to 48 hours |
| Amazon EC2 | 25, unless the account is already allowlisted | The same request form. Inbound SMTP to a Network Load Balancer is a separate case | AWS re:Post |
| OVHcloud VPS | 25 | A support request, or send on 587. A Local Zone VPS cannot reach any SMTP server, and that one has no unblock | VPS FAQ |
No VM was hired at these providers. Lists that still call OVH open are wrong: a VPS stays blocked until support opens it, and a Local Zone has no SMTP path. Contabo, Hostinger, UpCloud, IONOS and STRATO are left out.
Why the port is shut
They give the same reason. A new account on a cloud range is a cheap place to send spam, and the range pays for it when the mail is refused later. DigitalOcean, Hetzner, Vultr, Linode, Scaleway and OVH each say the block is there to keep that off the platform.
Opening the port on your VM leaves a neighbor's listing where it was. A shared range can already be on a blocklist because someone else on it sent junk. The ticket gets you a path. The reputation of the address is a separate problem, and so is the PTR. That record is the provider's. Gmail's permanent code when that record is missing or the forward lookup disagrees is 5.7.25. The three TXT records, once the packets can leave, are SPF, DKIM and DMARC for the 2026 Gmail and Outlook rules.
What to put in the request
Each provider asks for different facts. Send what that provider asks for.
Vultr wants the use, the spam controls you already have, and the volume you expect. They name SPF, DKIM and rate limits. Linode wants your name, the organisation if there is one, the use and how you will keep unwanted mail off the account, every domain you will send from, and a public link to the thing the mail is for. Hetzner Cloud wants the use, and it takes the request once the account is a month old and the first invoice is paid. The block follows the account: move the server to another account and the new owner's rule applies. Lightsail wants the use, a statement of how the account will keep unwanted mail from going out, the region, and optionally the static address and the reverse name. The form has to be sent as the root user, and a second region is a second form. AWS re:Post says that request can take up to 48 hours. That number is theirs. No wait was measured here.
Oracle's release note stops at "open a service limits request." Scaleway has no ticket once identity verification is done: the control is a checkbox, Enable SMTP, on the security group, and it applies to every instance in that group. A Hetzner dedicated server, after the month and the invoice, is a control in Robot. Before the four weeks are up, the contact form is only handled on weekdays between 08:00 and 18:00.
When the port stays shut
If the provider will not open port 25, or the request comes back refused, the mail has to leave through a relay on a port they still allow. Hetzner, Vultr, Google and OVH's VPS FAQ all point at that. On the machine, Postfix hands the queue to the relay on 587 and authenticates.
relayhost = [smtp.example.net]:587
smtp_sasl_auth_enable = yes
smtp_sasl_password_maps = hash:/etc/postfix/sasl_passwd
smtp_sasl_security_options = noanonymous
smtp_tls_security_level = encrypt
smtp.example.net stands in for the relay's hostname. The password file is hash: and then postmap. Those lines do nothing on a network that also drops 587. That is DigitalOcean, a Linode account under the restriction, and Scaleway before Enable SMTP. An OVHcloud Local Zone is stricter: the FAQ says it has no path to any SMTP server, and no unblock. Google, for a project that is not exempt, tells you to use 587 or 465, or a port of your own such as 2525 with an egress rule. Port 25 to the outside stays blocked there.
What a host should tell buyers
A buyer who is standing up mail needs the policy before the invoice, in the plan text: whether outbound 25 is open, whether 587 is open, whether a request exists, and who sets the PTR. The plan docs have no port 25 column.
The control sits on the provider side. At /infrastructure/network, the SMTP tab sets outbound SMTP for customer VMs on Proxmox and VirtFusion. SolusVM 2 keeps a cluster-wide switch in its own panel, and the tab is absent there. The customer's firewall screen has no copy of this policy. A VM set to Inherit follows the provider default. Allow and Block are explicit. New VMs start as Inherit.
When the policy blocks a VM, Proxmox gets guest-firewall DROP rules on outbound TCP 25, 465 and 587, and those rules sit ahead of the customer's own rules. VirtFusion gets a firewall ruleset whose name contains smtp, which the operator creates once. A DROP is why the customer sees a timeout. Their own firewall rules can still close the ports on a VM you have set to Allow. The provider block is the extra stop. The screen is documented under outbound SMTP controls.
FAQ
Does a reserved or floating IP get around the block?
On DigitalOcean the block includes traffic through a Reserved IP. On Hetzner Cloud the block is per account, so a second address on the same account is under the same rule. Moving the server to a different account applies that account's rule instead.
Does IPv6 skip it?
None of these providers exempts an IPv6 address. OVHcloud's Local Zone line is the wide one: no path to any SMTP server.
If they open port 25, will the mail stay out of spam?
The port is the path. Placement depends on the PTR the provider publishes for the address, on SPF, DKIM and DMARC, and on whether anyone else on that range has already burned it. Gmail's 5.7.25 is the missing or mismatched PTR.
Does port 587 work everywhere port 25 fails?
Hetzner leaves 587 open and says so. Vultr tells you to use 465 or 587 to an external relay. OVHcloud's VPS FAQ says to use 587, except on a Local Zone. DigitalOcean blocks 587. So does Linode, on the accounts that have the restriction, and so does Scaleway until Enable SMTP is ticked.
Is a Hetzner dedicated server open by default?
The Robot FAQ says outgoing 25 and 465 are blocked on all of those servers. After a month and a paid invoice you turn the ports on yourself in the administration interface. Port 587 is open without that step.